 WORLDTECH
Critical Google DevSite Flaw Allowed Attackers to Execute Remote Code Without Authentication
本文目前仅有英文版。
What happened
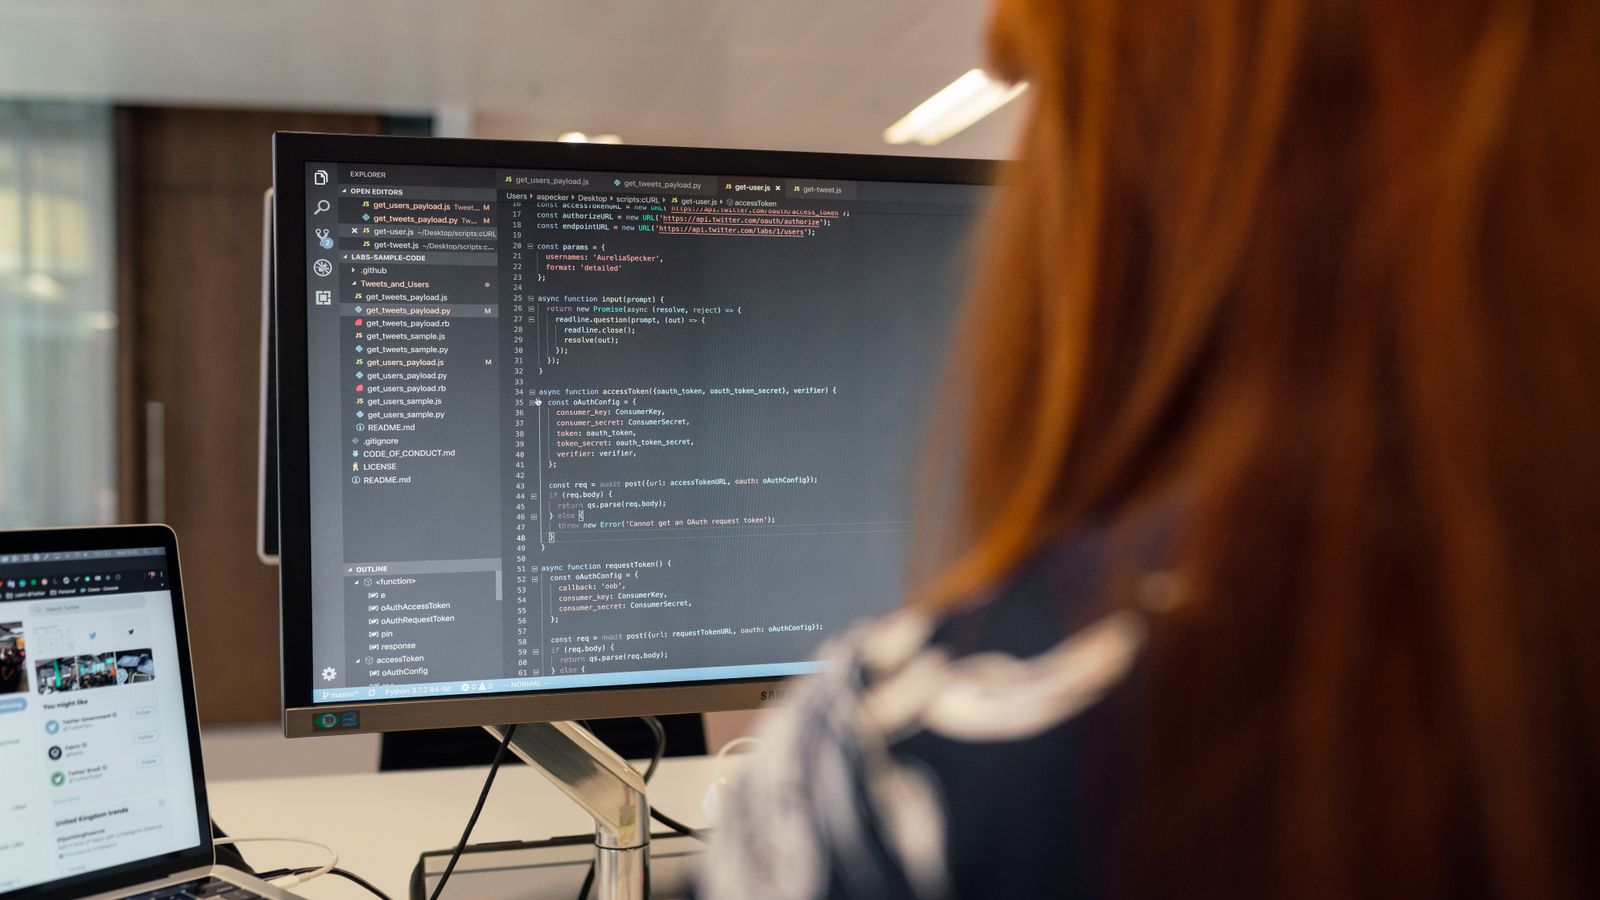
Security researcher Simon Köck discovered the issue while analyzing the OAuth authorization workflow used by Google’s developer documentation properties. After decoding the compressed payload, Köck found that the session included a serialized OAuth flow object containing Google OAuth client_id and client_secret values. Google is an Internet and software company based in Mountain View.
The vulnerability affected the shared infrastructure […] The post Critical Google DevSite Flaw Allowed Attackers to Execute Remote Code Without Authentication appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform . CVE/vulnerability Cyber Security News Vulnerabilities 2 min.
The vulnerability affected the shared infrastructure behind developers.google.com and other domains, including Firebase, Android Developer, Android Open Source Project, and Partner Android documentation sites. Google addressed the issue on October 7, 2026, awarding the researcher $90,000 through its Vulnerability Reward Program.
Critical Google DevSite Flaw The attack initiated with a request to the unauthenticated /oauth2/authorize endpoint on developers.google.com. This reuse meant that an attacker who recovered the client secret could generate valid signatures for any arbitrary session contents.
Key facts
- After decoding the compressed payload, Köck — found: that the session included a serialized OAuth flow object containing Google OAuth client_id and client_secret values
来源与证据
- GBHackers 报道来源
Critical Google DevSite Flaw Allowed Attackers to Execute Remote Code Without Authentication ↗
https://gbhackers.com/critical-google-devsite-flaw/